Privacy lab · DNS
DNS leak test: is your VPN really handling your lookups?
Every website you open starts with a DNS lookup. If those lookups go to a resolver outside your VPN, someone else can see which sites you look up. Here’s how DNS should travel, four ways it leaks, and how to check your setup.
CopVPN keeps DNS inside the VPN by default, with DNS leak protection in the apps for Windows, Mac, Linux, iPhone, iPad and Android.
30-day money-back guarantee (except crypto and manual payments)
Bench 01 · DNS leak test
Coming soonThe online test is on its way.
It will show results only from a real test on your connection, never sample data. Until then, the six checks below cover the same ground.
What the test will check
- 01Which DNS resolvers answer lookups from this browser
- 02Who operates them, where that can be identified
- 03Whether IPv6 lookups take a different route
The leak lab
Follow one lookup, then watch four ways it leaks
DNS turns a name like example.com into the address your device connects to. The resolver that answers can see every name you ask for. Pick a route to see where the lookup goes.
Route · Through the tunnel
Sealed- What happens
- Your lookup travels inside the encrypted tunnel to the CopVPN server and stays inside the VPN. Your provider sees encrypted traffic, not the name you looked up.
- Common cause
- Nothing leaks. This is how DNS should travel while you’re connected.
- What covers it
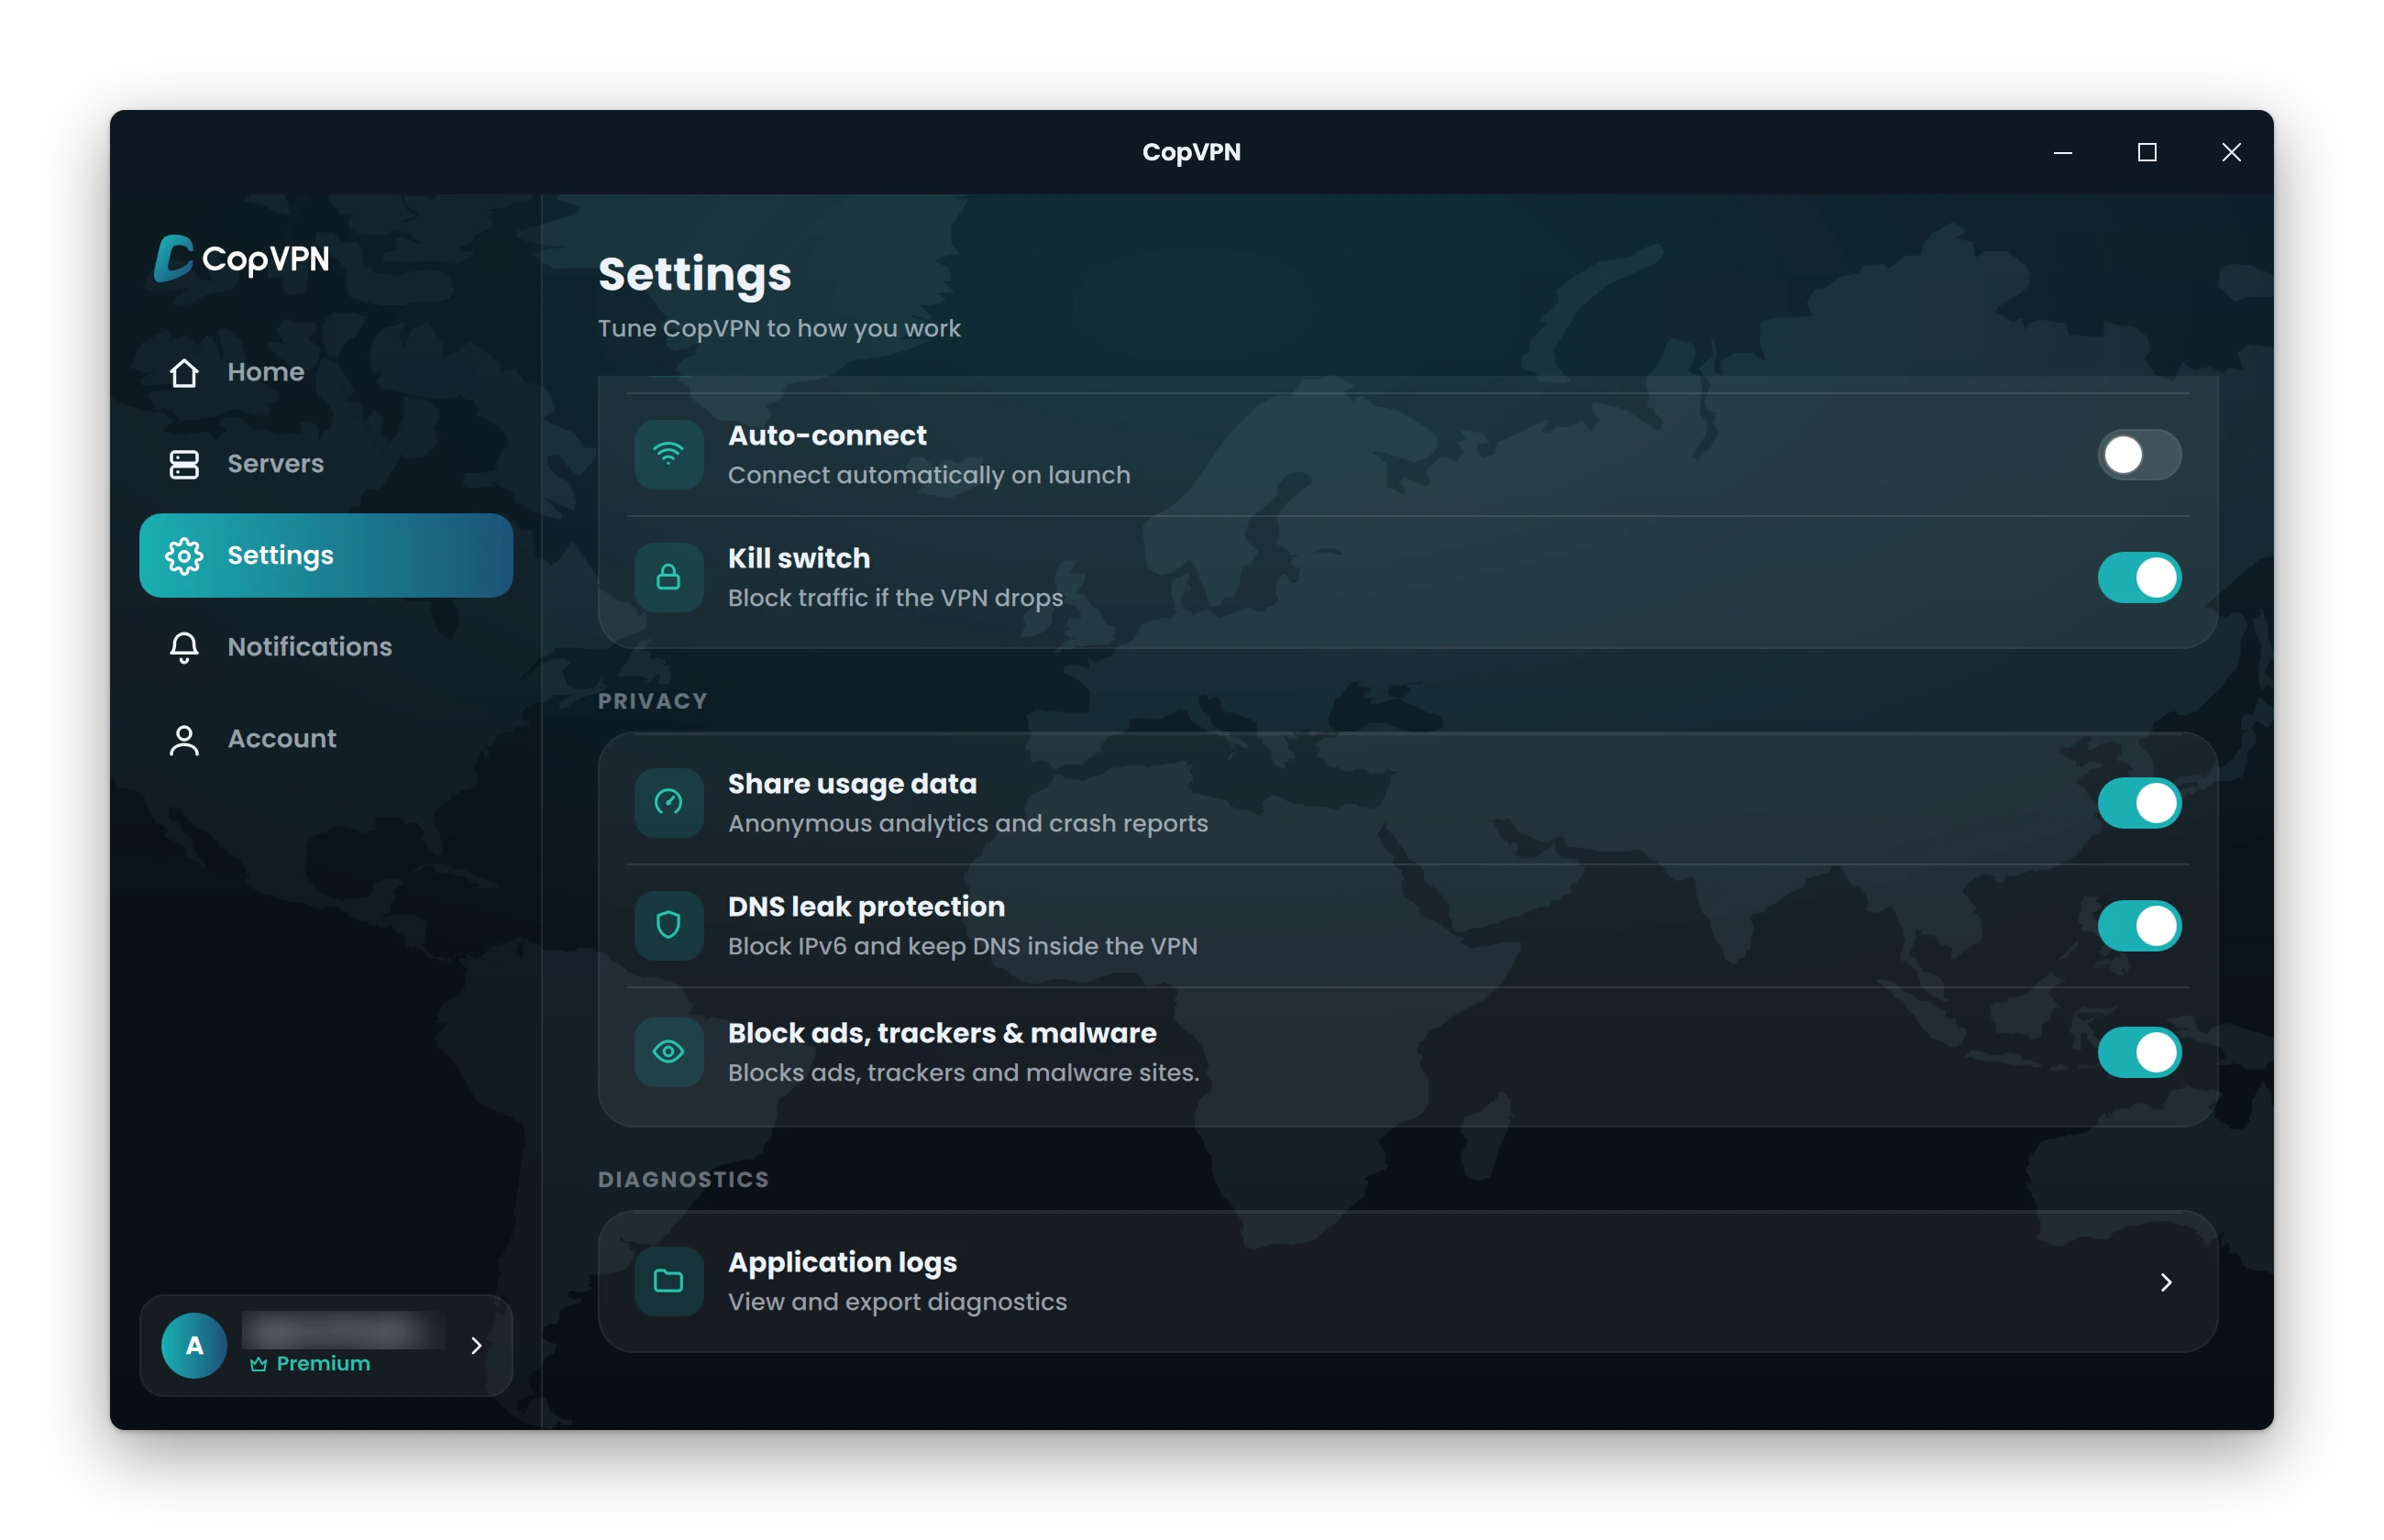
- DNS leak protection, “Block IPv6 and keep DNS inside the VPN”, on by default in the CopVPN apps for Windows, Mac, Linux, iPhone, iPad and Android.
- Start the six checks
WebRTC leaks are a different problem. WebRTC is a browser feature for calls and video that can reveal an IP address directly, without any DNS lookup. A DNS leak test won’t detect it, and a clean DNS result doesn’t rule it out. The CopVPN browser extension includes WebRTC leak protection.
Check your setup
Six checks, one at a time
Work through them in order. Select a step to see where it lives, tick it when it’s done, then check again.
All six checked. If a test still shows a resolver you don’t expect, email contact@copvpn.com and tell us which app and network you used.
Viewer
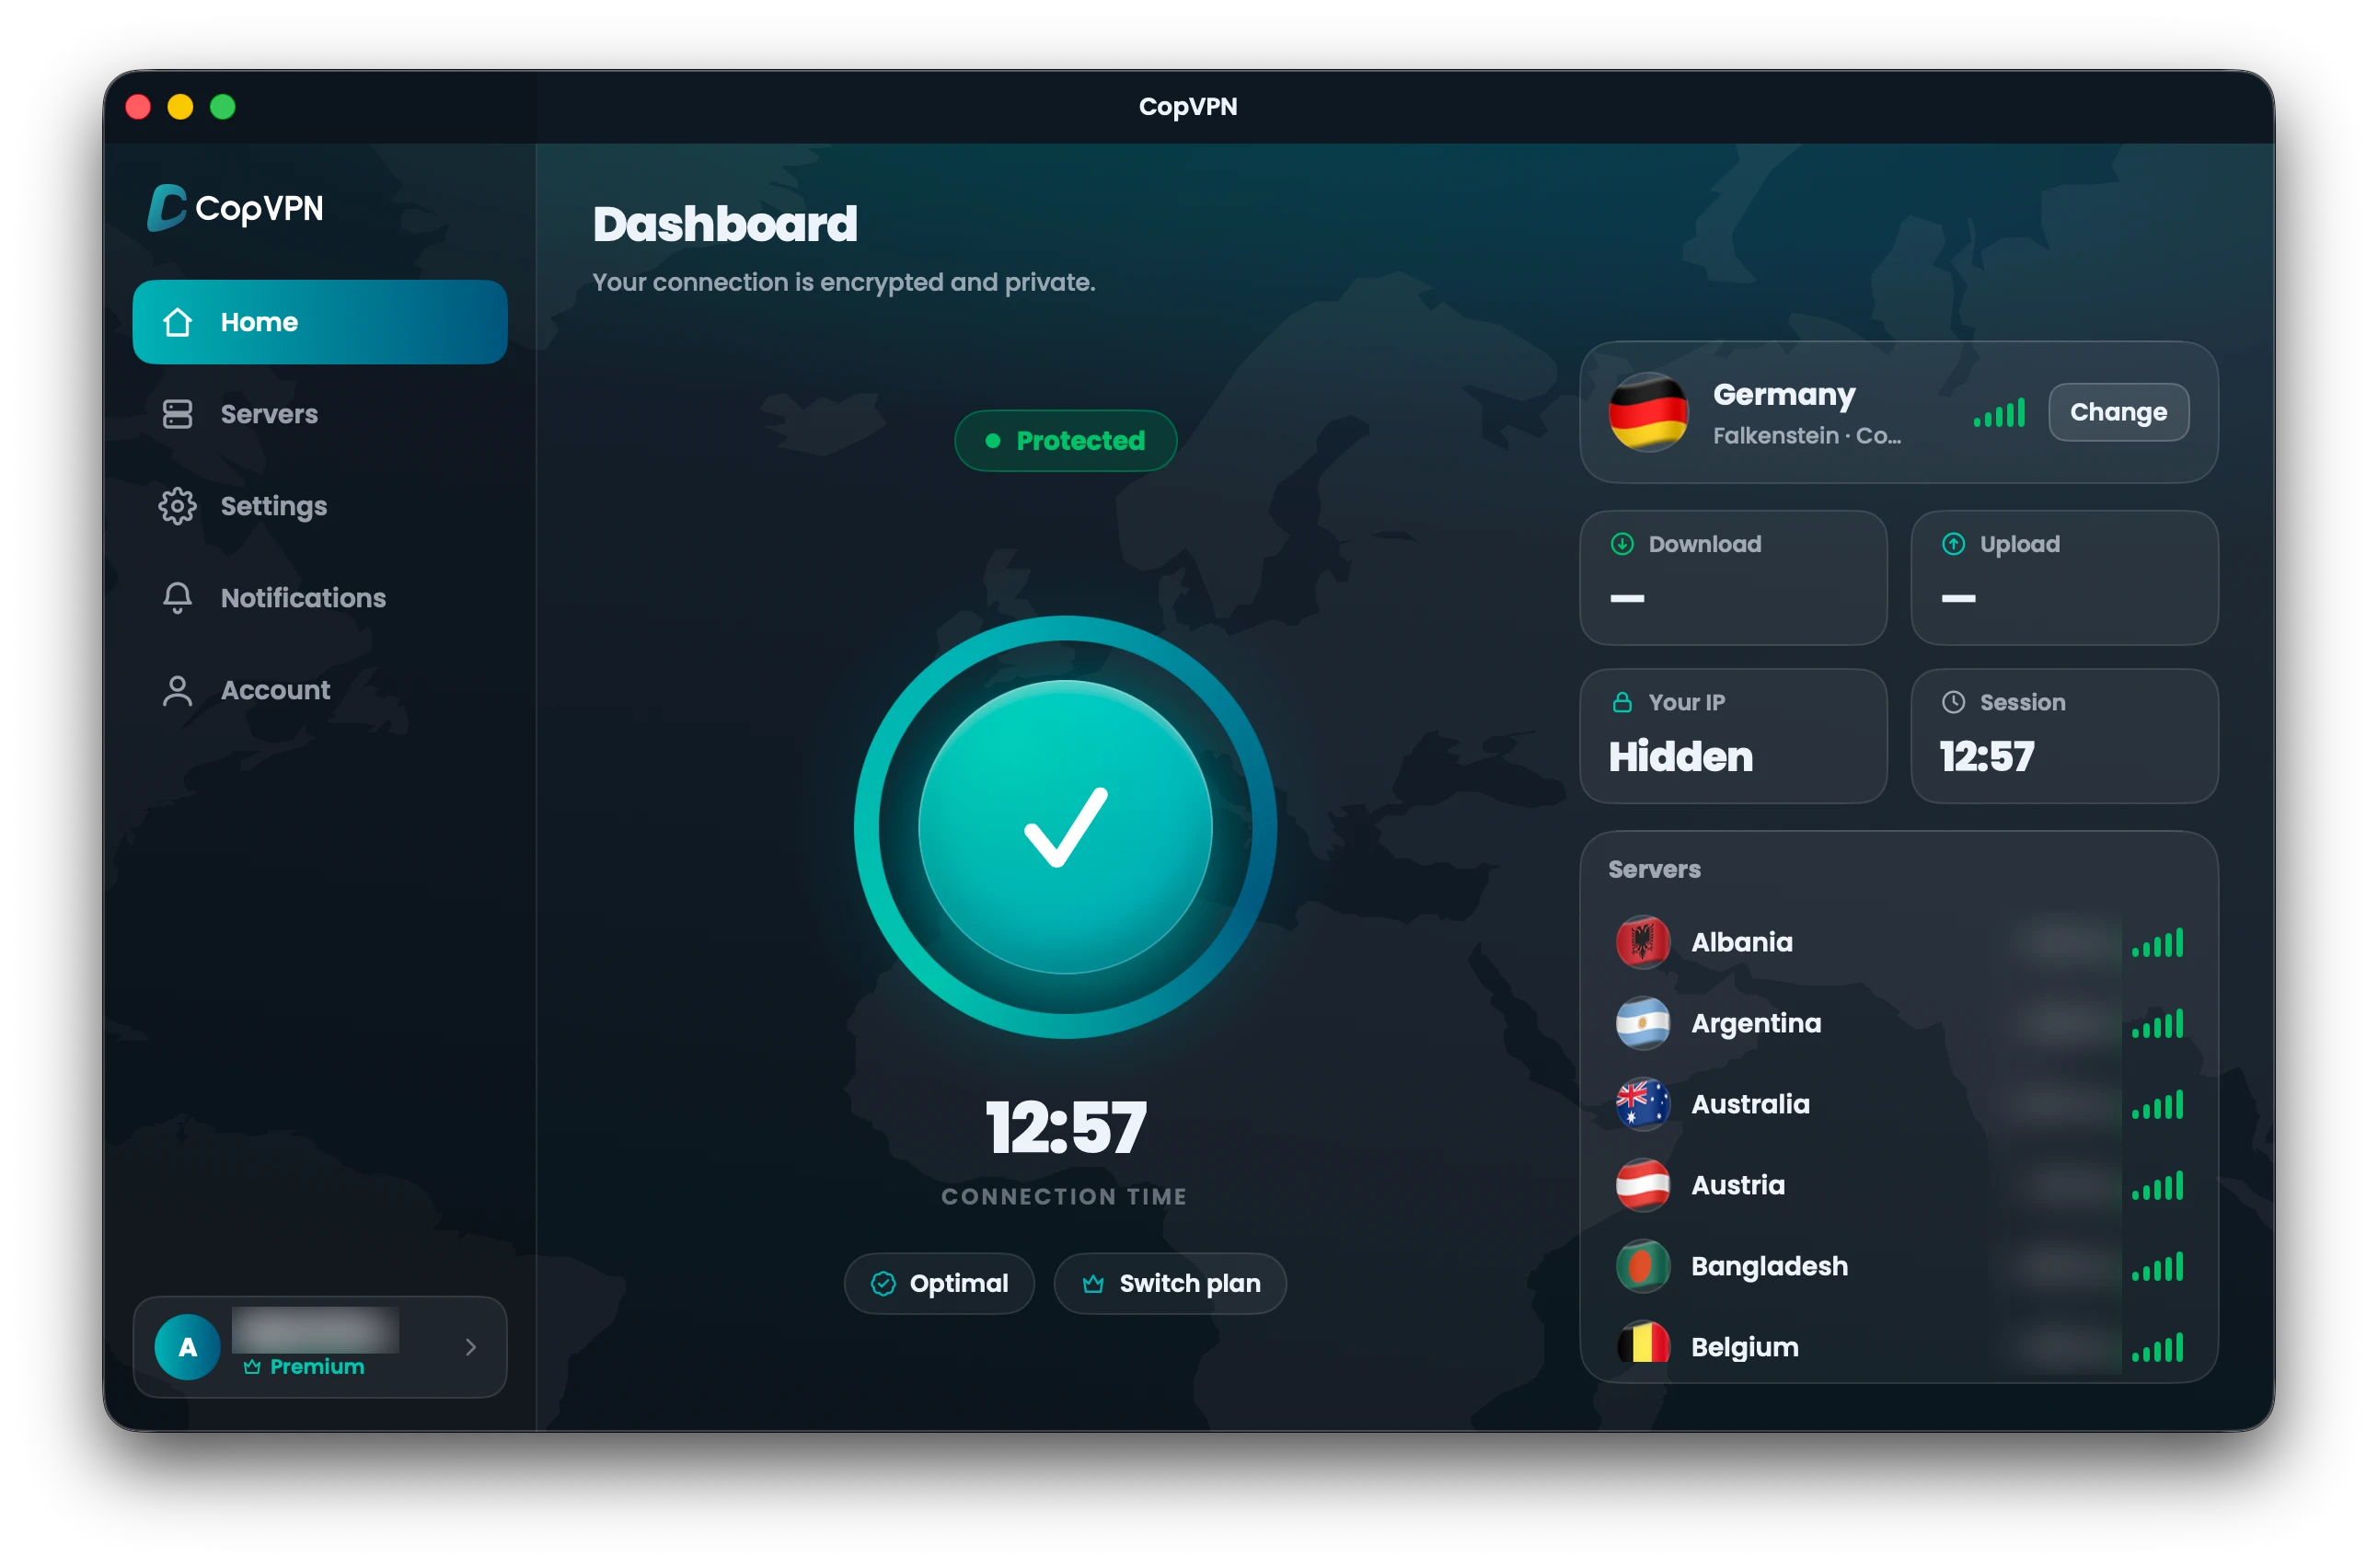
Step 1 of 6Where: Home
Step 2 of 6Where: Settings › DNS leak protection
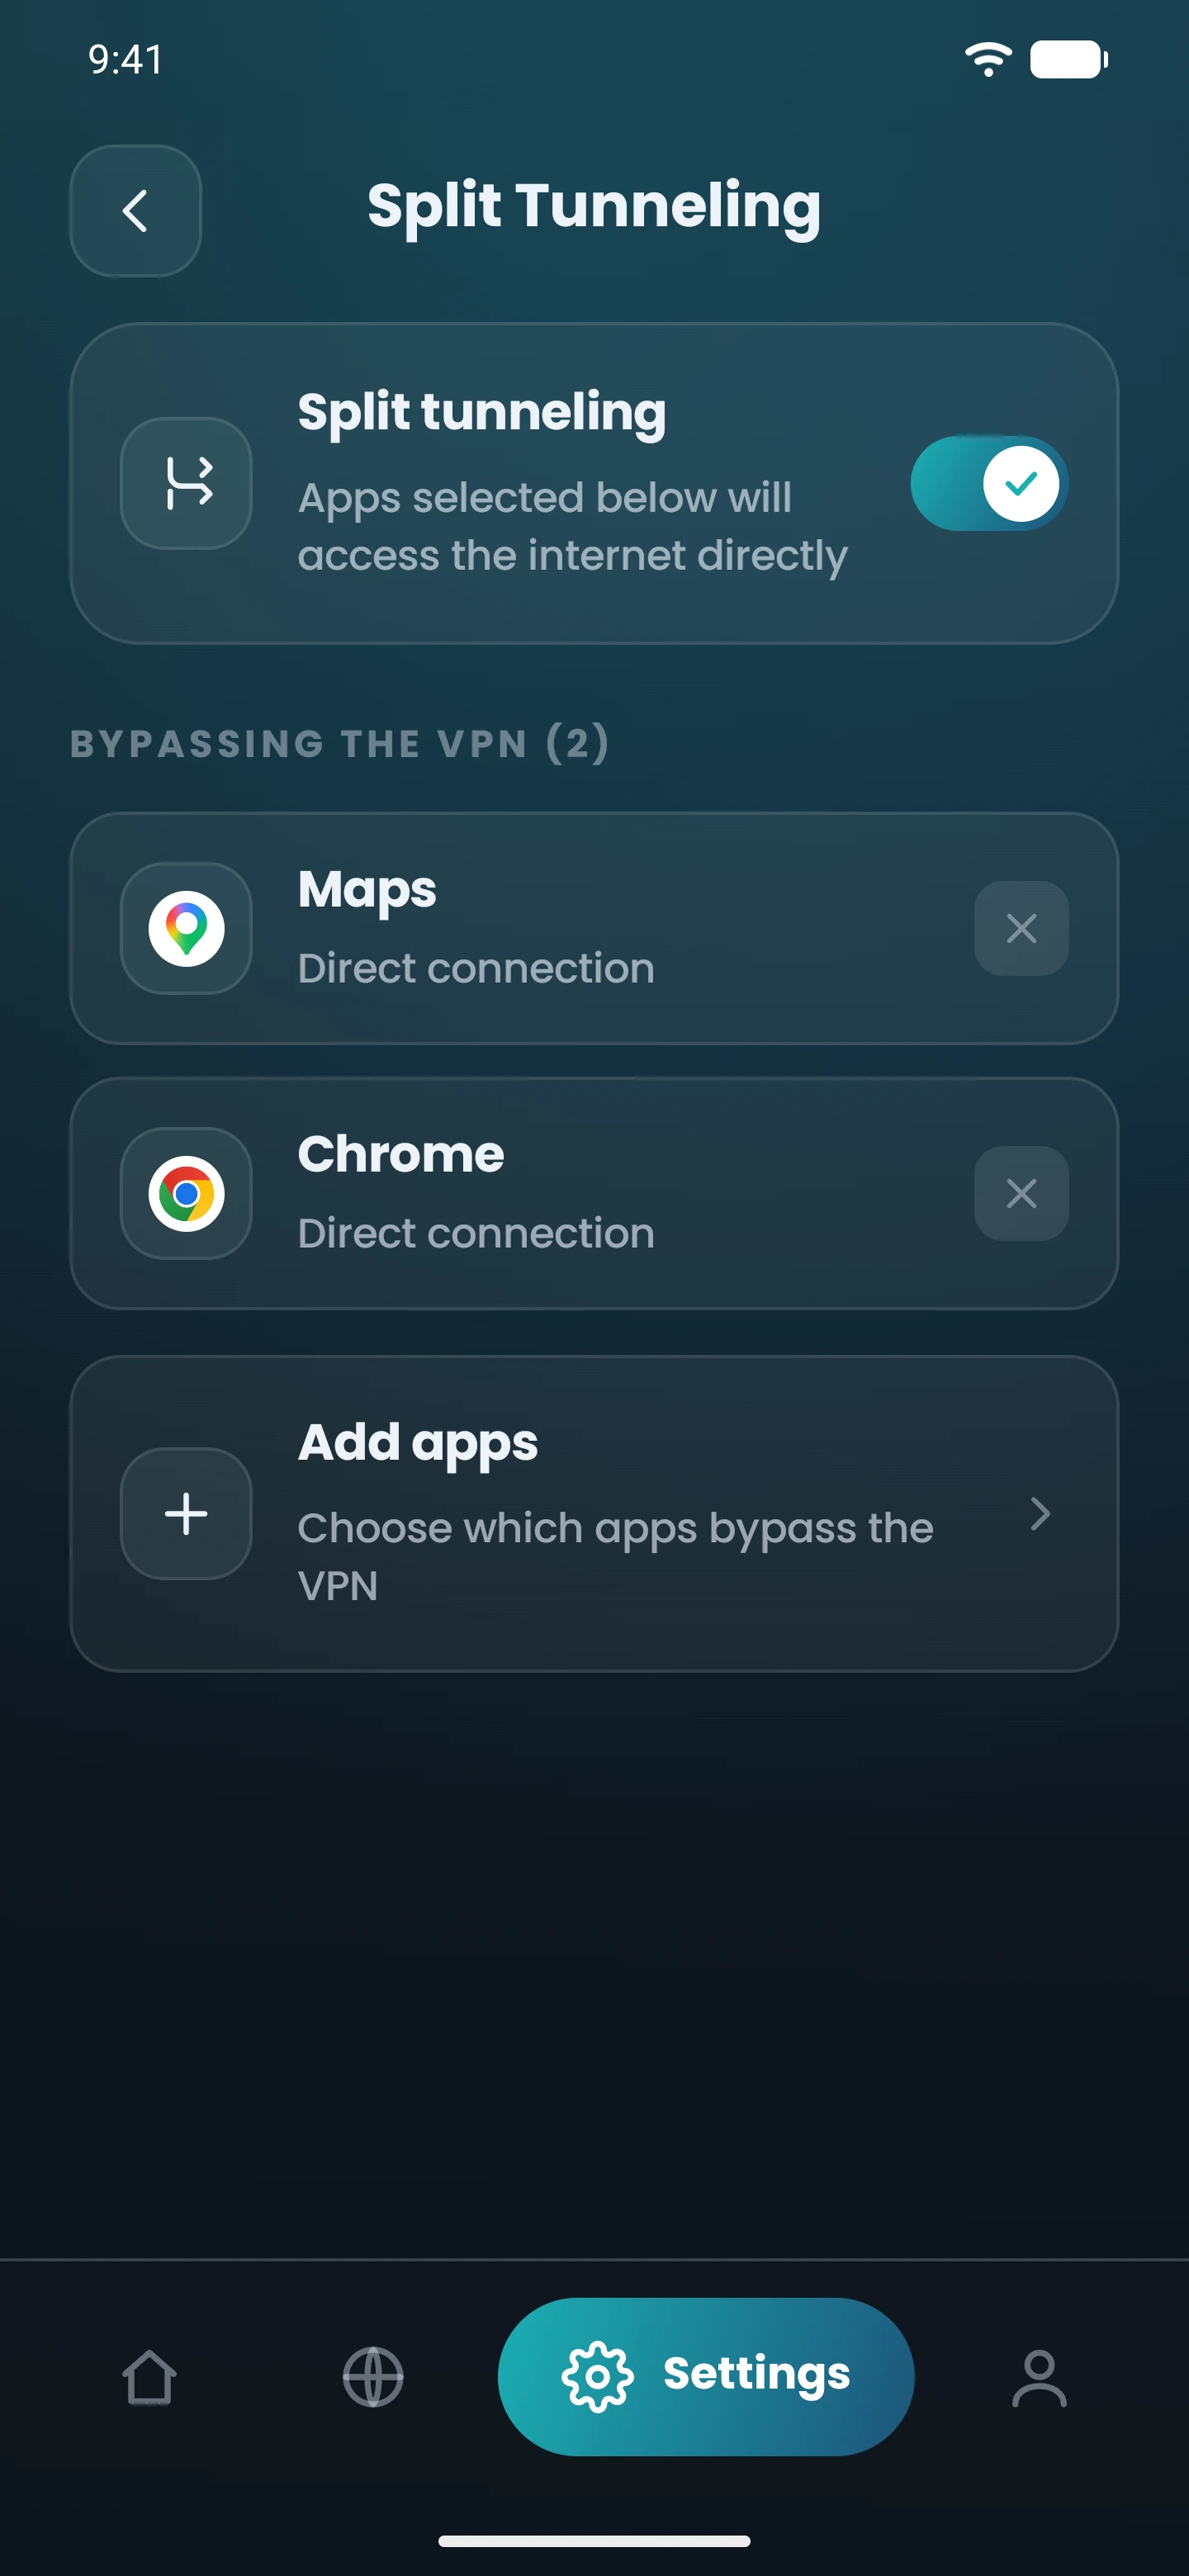
Step 3 of 6Where: Settings › Split tunneling
Step 4 of 6Where: Device and router network settings
Network settings
DNS server
Automaticuses the VPN’s while connected
Set by handcan override the VPN
On your device, and on your router
IllustrationStep 5 of 6Where: Browser settings › Secure DNS
Browser settings › Privacy
Secure DNS
Use your system DNSwhile you test
Use the browser’s providermay answer outside the VPN
In each browser you use
IllustrationStep 6 of 6Where: Home › connect
- Disconnect
- Reconnect
- Check again
In the CopVPN app
IllustrationReading a result
What a DNS leak test tells you, and what it can’t
Scope sheet
DNS leak test · applies to any test you run
In scope: a test can show
- IN-01Which DNS resolvers answered lookups from this browser, on this network, right now.
- IN-02Who operates those resolvers, where that can be identified reliably.
- IN-03Whether IPv6 lookups take a different route from IPv4.
- IN-04Whether the result changes when you connect or disconnect the VPN.
Out of scope: a test can’t show
- OUT-01That every app on your device uses the same DNS route. Apps and browsers can set their own.
- OUT-02That a resolver is a problem because of its location. A server in another country is normal for a VPN.
- OUT-03Your browsing history. A test only uses its own one-time hostnames.
- OUT-04Anything about WebRTC or other IP leaks.
A clean result is a good sign, not a full check of your connection. Read what a VPN hides and what it doesn’t, and turn on the kill switch to block traffic if the VPN drops.
What is a DNS leak?
A DNS leak is when your device sends DNS lookups to a resolver outside your VPN, usually your provider’s, while the VPN is connected. That resolver can see which hostnames you look up.
How can I check for a DNS leak?
Connect your VPN and run a DNS leak test. If any resolver in the result belongs to your provider, or to another operator you didn’t expect, lookups are going outside the tunnel. Our own test is on its way to this page.
Can a DNS leak test prove my VPN is working?
No. It checks one thing: where DNS lookups go from this browser, on this network. A clean result is a good sign, not a full check of your connection.
Why do I see more than one DNS server?
Large DNS services spread lookups across several servers, so seeing two or more from the same operator is normal. What matters is who operates them.
Is a DNS server in another country a problem?
No. When you connect to a VPN server abroad, its resolvers are usually there too. Location alone doesn’t mean a leak; an unexpected operator does.
Does a DNS leak reveal every website I visit?
It reveals the hostnames looked up through the leaking resolver, not page contents or full addresses. Sites you visit over HTTPS stay encrypted.
How does CopVPN prevent DNS leaks?
DNS leak protection, “Block IPv6 and keep DNS inside the VPN”, is on by default in the CopVPN apps for Windows, Mac, Linux, iPhone, iPad and Android. On Android TV it’s always on. The browser extension sends site lookups through CopVPN while it’s connected.
Keep reading
Related features and guides
Plans
DNS that stays inside the VPN
DNS leak protection is on by default in every CopVPN app that has the setting. Plans run from 1 month to 5 years.
30-day money-back guarantee (except crypto and manual payments)We follow a no-logs policy